Methodology

PingCastle is where Netwrix Directory Security starts ↗. Free AD risk discovery that feeds directly into continuous monitoring, threat detection, and recovery. Built from experience securing hundreds of domains, the methodology gives teams a practical path to bring Active Directory risk under control.

Mascots climbing an orange stairway
Step 1

Understand the stakeholders

There are two main stakeholders in the Active Directory landscape: Management, which holds budget decisions, and Operations, which ensures Active Directory stays up and running.

Management needs
Assess current security level · avoid critical risks · prioritize the action plan
Operations needs
Detect critical security issues · overview of the technical situation · guidance to fix issues
Maturity based Improvement — management needs a tool to translate data into risk; operations need a tool to solve problems and increase maturity.
Step 2

Prepare the battle plan

Inspired from CMMI — a well-known Carnegie Mellon methodology to evaluate maturity on a grade from 1 to 5, adapted here to Active Directory security.

View document
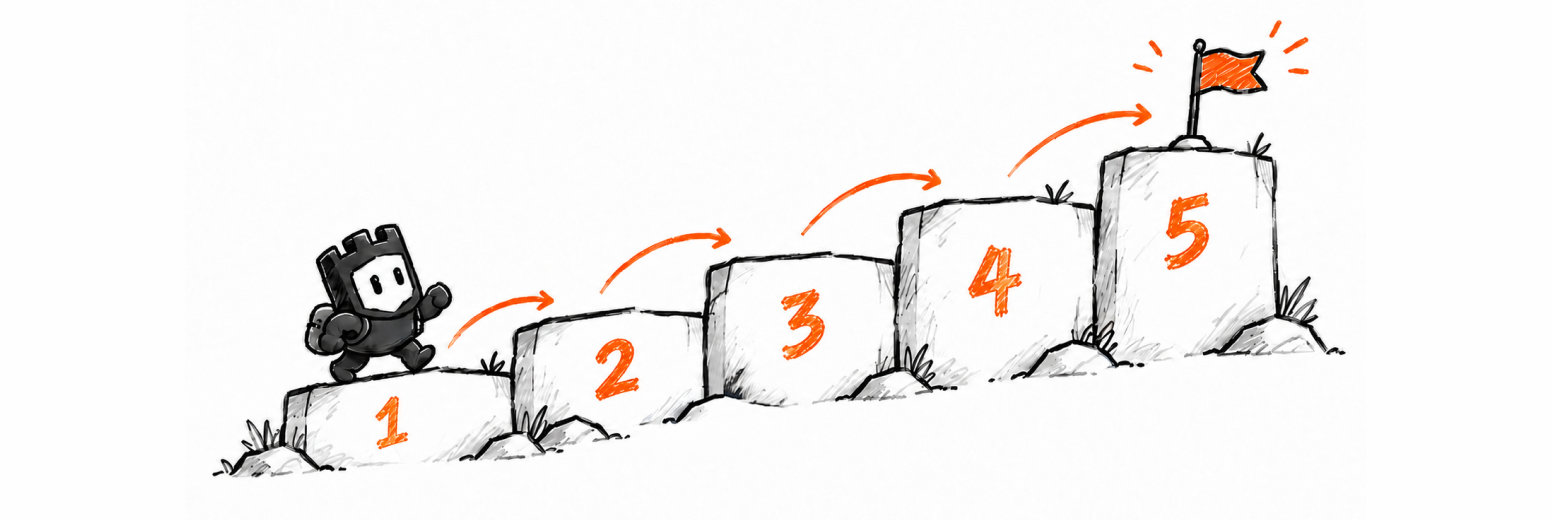
Mascot climbing stone steps toward a flag, representing the maturity path
Step 3

Know your backyard

The goal is to reach Level 1 by defining the “scope” — the set of domains to put under control — through a discovery phase covering three areas:

Domain coverage
Do you actually know how many domains you have in your Active Directory?
Ownership
Is every domain actually monitored by someone?
External trusts
Are domains exposed on the internet without protection?
Focus on domain discovery to get management support — prevent forgotten domains or trusts to companies you don't control.
Step 4

Perform security controls periodically

The goal is to reach Level 2 by defining “periodic controls” that guarantee a minimum control level and avoid critical changes going unnoticed.

Internal trusts
Badly implemented trusts risk major cross-contamination.
Risk score control
Are you aware of every possible security issue in your Active Directory?
Establish baseline to secure budget allocation — get a health check every week, request SID Filtering on 100% of trusts, set a risk-score reduction target.
Step 5

End-to-end directory security

Assessment tells you where the risk is. It doesn't fix it, it doesn't stop someone exploiting it, and it can't undo the damage if they do. This is where PingCastle hands off to the rest of Netwrix Directory Security.

From assessment to full directory protection
Automate directory management
Replace manual joiner, mover, and leaver tasks with policy-driven automation. Accounts and group memberships stay accurate, and stale access doesn't pile up between audits.
Enforce least privilege
Remove standing admin rights and give elevated access only for the task at hand. Privileged sessions are recorded, so you can show who did what.
Monitor
Near real-time change tracking, so a misconfiguration or new trust doesn't sit unnoticed until next week's report.
Detect & respond to threats
Detect & respond to attack techniques in progress — not just the vulnerabilities that make them possible.
Recover
Recover AD, Entra ID and Okta objects and attributes, or entire AD forests, minimizing downtime and business impact.

Together, these turn a maturity model into a living control system: assess, automate, enforce, monitor, detect, respond, recover.

PingCastle's health check is free and takes minutes to run. When you're ready to move from periodic assessment to continuous protection, Netwrix extends the same maturity model into automated directory management, least-privilege access, full-time monitoring, detection, and recovery, on-premises and in Entra ID.